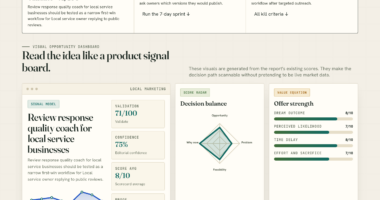
📊 Full opportunity report: How To Safeguard Remote Work Devices With SMB Endpoint Security on IdeaNavigator AI — validation score, market gap, and execution plan.
TL;DR
A new SMB endpoint security tool offers a lightweight agent for remote teams to verify device encryption, updates, and security settings. It helps meet compliance standards like SOC 2 without heavy management tools.
A new lightweight agent designed for remote teams is being tested to verify device security posture on employee-owned hardware, addressing a critical gap for SMBs facing compliance audits and security challenges.
The security checker, developed by IdeaNavigator AI, targets SMBs with remote employees using mixed hardware environments, including Macs, Windows laptops, and unmanaged phones. It provides a voluntary, installable agent that assesses disk encryption, OS updates, screen lock status, and password manager presence. The tool reports pass/fail results to a centralized dashboard, enabling security teams to identify vulnerabilities without relying on invasive mobile device management (MDM) solutions.
This approach responds to growing compliance demands, such as SOC 2 audits, which require proof of device security measures. Currently, many SMBs lack visibility into the security status of employee-owned devices, risking non-compliance and data breaches. The tool aims to fill this gap by offering a lightweight, non-intrusive way to verify device security posture and facilitate self-remediation.
Early validation involves deploying the agent at ten remote startups, measuring device enrollment rates, and confirming that auditors accept the generated reports as sufficient evidence of compliance. The product is offered on a per-device monthly pricing model, with optional compliance report exports for paid tiers.
Implications for SMBs’ Remote Security Compliance
This development could significantly improve security posture management for SMBs, which often lack the resources for comprehensive device management. By enabling quick, voluntary checks of employee devices, companies can better demonstrate compliance during audits, reduce the risk of data breaches, and improve overall security hygiene. The approach offers a scalable, less invasive alternative to traditional MDM solutions, which can be too heavy-handed for employee-owned devices, especially in remote work settings.
As remote work continues to expand, ensuring device security without disrupting employee privacy or productivity becomes increasingly critical. This tool provides a practical solution to verify security controls like encryption and updates, which are often overlooked in decentralized environments. Its success could influence broader adoption of lightweight security verification methods across the SMB sector.
device encryption verification tool
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Need for SMB Endpoint Security Solutions
Remote work has accelerated over the past few years, leading SMBs to face new security and compliance challenges. Unlike large enterprises, many SMBs lack dedicated IT teams or extensive device management infrastructure. As a result, they often rely on employee-owned hardware with minimal oversight, creating gaps in security protocols such as disk encryption, OS updates, and screen locks.
Regulatory frameworks like SOC 2 increasingly demand proof of security measures on all devices handling sensitive data. Heavyweight mobile device management (MDM) tools, which can enforce policies remotely, are often too invasive or complex for SMBs and employee-owned devices. This leaves a verification gap that can jeopardize compliance and increase vulnerability to breaches.
The proposed device security checker aims to address this gap with a lightweight, voluntary agent that provides visibility into device security status without requiring invasive management or extensive employee onboarding. Early pilots are testing its acceptance and effectiveness in real-world SMB environments.
As an affiliate, we earn on qualifying purchases.
Uncertainties About Adoption and Compliance Acceptance
It remains unclear how widely SMBs will adopt this solution and whether auditors will accept the reports as sufficient evidence of security posture. The pilot program is ongoing, and broader validation is needed to confirm effectiveness and compliance acceptance across different regulatory environments.
employee device security audit software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps for Validation and Market Adoption
The company plans to expand testing to more SMBs, gather feedback, and refine the agent’s capabilities. If pilot results are positive, a wider rollout could follow, with additional features such as automated remediation guidance. Monitoring how auditors view these reports will be crucial for scaling adoption.
lightweight endpoint security agent
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
How does the device security checker work?
The agent is a voluntary, installable software that assesses device encryption, OS updates, screen lock status, and password management. It reports results to a dashboard for security teams to review.
Is this solution suitable for all types of devices?
The current focus is on common employee devices such as Macs, Windows laptops, and unmanaged phones, with plans to expand support based on demand.
Will this replace traditional MDM solutions?
No, it is designed as a lightweight, non-intrusive supplement for SMBs that cannot or do not want to deploy full MDM solutions on employee-owned devices.
What are the security benefits of using this tool?
It helps verify critical security controls like disk encryption and OS updates, reducing the risk of data breaches and non-compliance during audits.
When will the product be generally available?
The pilot program is ongoing; a wider commercial release is expected after successful validation and feedback collection, likely within the next few months.
Source: IdeaNavigator AI