TL;DR

Get hardware and tech essentials delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
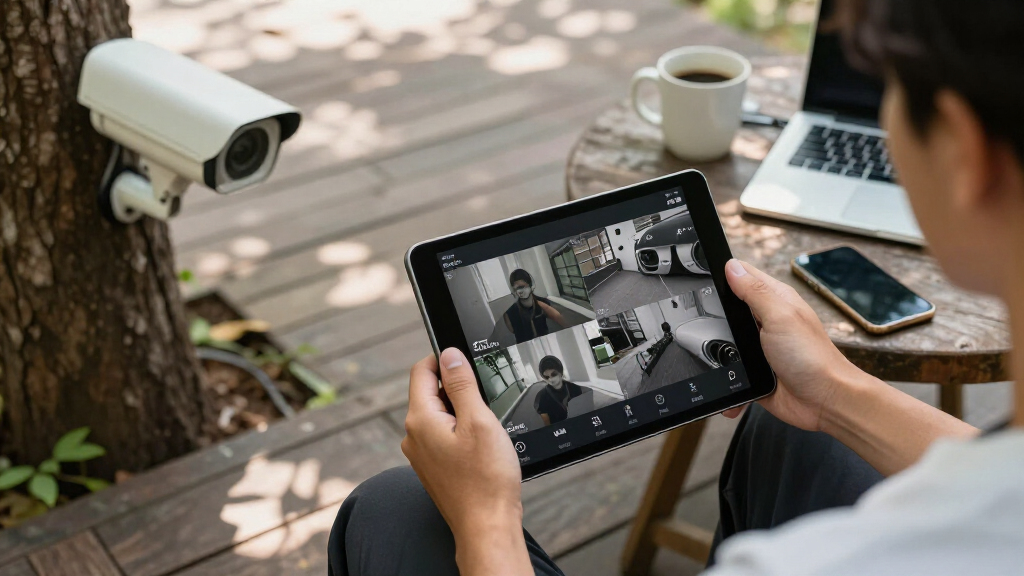
Security researchers discovered that certain security cameras are exposing GitHub admin tokens on their login pages. This vulnerability could allow attackers to compromise device management and access sensitive data, raising urgent security concerns.
Security researchers have identified a vulnerability where certain security cameras are shipping with embedded GitHub admin tokens visible on their login pages. This flaw could enable malicious actors to access device management interfaces, posing a significant cybersecurity risk for organizations relying on these devices. The discovery highlights the growing challenge of managing emerging device vulnerabilities in connected security systems.
The vulnerability was uncovered by cybersecurity analysts examining the firmware and web interfaces of various security cameras. They found that some models include hardcoded or embedded GitHub admin tokens, which are displayed in the login page source code. These tokens could potentially be exploited by attackers to gain control over the devices or access associated management dashboards.
According to initial reports, the presence of these tokens was confirmed on multiple camera models from different manufacturers. The tokens are used for firmware updates and device management processes, but their exposure in the login interface makes them accessible to anyone inspecting the web pages. Cybersecurity experts warn that such exposure significantly increases the risk of unauthorized access and device hijacking.
Manufacturers have not yet issued official statements about the flaw, and it is unclear how widespread the issue is across different product lines. Experts advise organizations to review their device configurations and monitor for signs of exploitation, especially if their security cameras are accessible over the internet.
Implications for Organizational Security and Device Management
This discovery underscores the importance of secure device configuration and management in the growing ecosystem of connected security hardware. Exposure of admin tokens can lead to unauthorized device control, data breaches, and potential infiltration of organizational networks. Small and mid-sized organizations, which may lack dedicated cybersecurity teams, are particularly vulnerable to such overlooked vulnerabilities.
It also highlights the need for manufacturers to follow best security practices, including avoiding hardcoded credentials and ensuring sensitive tokens are not exposed in web interfaces. The incident raises awareness about the risks posed by seemingly minor security oversights in connected devices.
As an affiliate, we earn on qualifying purchases.
Rising Risks from IoT and Connected Security Devices
Over the past few years, the proliferation of Internet of Things (IoT) devices, including security cameras, has expanded the attack surface for organizations. Many devices are shipped with default or embedded credentials, often poorly secured, leading to frequent vulnerabilities. Recent incidents have shown that attackers can leverage exposed tokens and credentials to compromise entire networks.
This case adds to a growing list of security flaws in consumer and enterprise IoT devices, emphasizing the need for rigorous security testing and updates. While the specific issue of exposed GitHub tokens is new, it fits within a broader pattern of security lapses in connected hardware.
Security researchers have called for stricter supply chain security and better firmware management to prevent such vulnerabilities from reaching end users.
“The presence of embedded GitHub tokens in device login pages is a serious oversight that could lead to widespread device compromise if exploited.”
— an anonymous cybersecurity researcher
As an affiliate, we earn on qualifying purchases.
Extent of the Vulnerability and Manufacturer Response
It is not yet clear how many models are affected or whether manufacturers are aware of the issue. No official statements have been issued, and details about the scope of the exposure remain limited. The potential for active exploitation is also still being assessed.
security camera with encrypted firmware
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Monitoring, Response, and Manufacturer Remediation Efforts
Security researchers and affected organizations will continue to investigate the scope of the vulnerability. Manufacturers are expected to release patches or updates to mitigate the risk. Organizations are advised to monitor for updates, review device configurations, and implement network security best practices.
Further disclosures or official responses from device makers are anticipated in the coming weeks as the issue is evaluated and addressed.
professional security camera system
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
How serious is the risk posed by exposed admin tokens in security cameras?
The risk is significant because exposed tokens could allow attackers to control devices, access sensitive footage, or use the devices as entry points into organizational networks.
Are all security cameras vulnerable to this issue?
It is currently unclear how widespread the vulnerability is. The issue has been confirmed on multiple models, but further investigation is needed to determine the full scope.
What should organizations do immediately if they suspect their devices are affected?
Organizations should review device configurations, disable internet access if possible, and monitor network activity for signs of compromise. They should also stay alert for firmware updates from manufacturers.
Will manufacturers release patches to fix this vulnerability?
Manufacturers are expected to evaluate the issue and release security updates or patches. Monitoring official channels for announcements is recommended.
Does this vulnerability affect consumer-grade security cameras as well?
The initial findings focus on certain enterprise or small-business models, but similar issues could exist in consumer devices. Users should check for updates and review device security settings.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.