🔍 Read the full analysis: The Route From PHP2Shell To Wiper On Check Point Gateways on ThorstenMeyerAI.com

Get hardware and tech essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
Check Point says attackers exploited unpatched Security Gateways from October 30 to November 4, using PHP2Shell flaws to get in and a separate vulnerability to gain root access. In some Israeli-targeted incidents, attackers reached VMware ESXi servers and ran a wiper; a second wave across multiple countries showed no evidence of destructive activity. Check Point published a Jumbo Hotfix on November 12, and the attacker’s identity remains unconfirmed.
Attackers used PHP2Shell vulnerabilities and a separate root-access flaw to compromise unpatched Check Point Security Gateways between October 30 and November 4, the company said. In some incidents, attackers moved from gateways to VMware ESXi servers and ran a wiper that destroys data; Check Point says it has not identified the attackers with confidence.
Check Point’s November 12 investigation describes a two-stage compromise. Attackers first reached the Mobile Access portal on gateways that had not received the available PHP2Shell hotfix. The two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, could allow unauthenticated remote code execution. Check Point reported indicators including marked PHP session files and repeated crashes in portal web workers.
After gaining code execution under the portal’s service account, attackers used CVE-2026-123039 to obtain root privileges on the appliance. Check Point says the Gaia DynamicCLI helper ran as root and accepted commands through a world-writable local socket without checking the caller. The company rates the flaw 7.8 out of 10, high severity; exploitation required code execution on the appliance first.
Check Point says the first observed wave targeted Israeli organizations. In some cases, attackers moved to a VMware ESXi host and ran a wiper called destroy_v6, which overwrites files with zeros before deleting them. Its note, DREAM_ANNEXATION.txt, rejects ransom negotiations. A second wave on November 2 targeted organizations in several countries, but Check Point said it found no evidence of destructive activity in that wave.
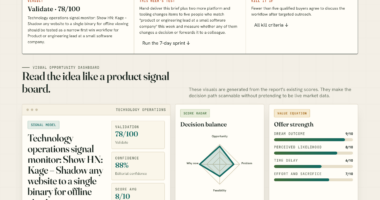
Check Point gateway attacks · Oct 30 – Nov 4, 2026
How the break-in worked, and where the fix cuts it
The attack chain as Check Point describes it, without the technical recipe. One update closes the first two doors.
Path through the network (schematic)
InternetAttacker traffic
Gateway web portalMobile Access
Gateway systemRoot rights
Internal networkScanned from the gateway
VMware ESXi hostRuns virtual machines
normaltaken overwipedclosed by fix
Step by step
- Scanfrom Oct 30Unpatched gateways with an internet-facing Mobile Access portal are probed
- Way inPHP2Shell (CVE-2026-109618, CVE-2026-109619) runs code as the portal’s service account closed by fix
- RootCVE-2026-123039 in DynamicCLI turns that into full root rights closed by fix
- Back doorWeb shells in the portal’s login-page folder; TSGA back door with TSProxy hidden in appliance processes
- ReconThe gogo scanner maps internal systems from the gateway
- WipeSSH to a VMware ESXi host, destroy_v6 wiper, a note that rejects ransom talk (first wave, some victims)
R82.20 from Take 14 · R82.10 from Take 52 · R82 from Take 132 · R81.20 from Take 174. It closes both PHP2Shell and CVE-2026-123039. Then check for signs of compromise.
Sources: Check Point Research, “PHP2Shell Exploitation on Check Point Gateway”, and Check Point advisories sk1000302 and sk1000362, Nov 12, 2026. Schematic of the attack path described by Check Point, not a map of any victim’s network.
Graphic: Powered by Thorsten Meyer AI
Gateway Breaches Reached Virtual Servers
The incidents show how a vulnerable internet-facing gateway can serve as an entry point to systems beyond the appliance itself. In the cases Check Point described, attackers moved from a network security device to an ESXi host, where destructive malware could affect hosted workloads and data. The report does not establish how many downstream systems were affected.
There is also a patching distinction for defenders: Check Point says a PHP2Shell hotfix was available on October 23, before the observed attacks began, while the separate root flaw and its fix were disclosed on November 12. Installing the earlier fix alone would not address CVE-2026-123039. The company’s current guidance is to install the November Jumbo Hotfix and inspect exposed gateways for signs of compromise.
CISA added CVE-2026-123039 to its Known Exploited Vulnerabilities catalog on November 13 and set November 16 as the deadline for U.S. federal agencies to act. That listing signals a requirement for those agencies; other organizations should use Check Point’s advisory to guide their own response.
Products Worth Considering

Amazon Kindle Scribe (32GB) with Premium Pen, Tungsten (Like-New)

Anker SOLIX C1000 Gen 2 Portable Power Station with 100W Solar Panel
Samsung 57 Odyssey Neo G9 (G95NC) Dual 4K UHD 1000R Curved Gaming Monitor
As an affiliate, we earn on qualifying purchases.
Two Flaws, Two Patch Timelines
PHP2Shell refers to two critical flaws in PHP. The PHP project released fixes on October 21 in versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. CISA describes the flaws as allowing unauthenticated remote code execution and added them to its exploited-vulnerabilities catalog on October 26. PHP is embedded in many products, so users often depend on each vendor to incorporate the fix into its own software and release an appliance update.
For Check Point gateways, the PHP flaws provided the initial route into the portal, while CVE-2026-123039 provided root access after code execution had already been achieved. Check Point says it released a PHP2Shell hotfix on October 23, but disclosed and fixed the root-access flaw in its November 12 Jumbo Hotfix. The distinction matters when checking whether systems received a complete remediation.
Check Point’s stated patch levels include at least Take 14 for R82.20, Take 52 for R82.10, Take 132 for R82 and Take 174 for R81.20. The vendor says to prioritize internet-facing Mobile Access portals, update Management Servers and Security Gateways, and check exposed devices for its listed indicators. R81.10 and older versions are past end of support, according to the source material.
“Only a couple of dozen unpatched systems, in a single region, were compromised in the observed incidents.”
— Check Point
Attribution and Damage Remain Open
Check Point has not attributed the operation to a threat actor with confidence. The back door, TSGA, belongs to a malware family that ESET has linked to a China-nexus group, according to the source material. However, the destructive activity aimed at Israeli organizations does not fit that group’s known interests, leaving the connection unresolved rather than establishing who carried out the attacks.
The company reported that only a couple of dozen unpatched systems in one region were compromised in the incidents it observed. The available account does not specify the total number of organizations targeted, whether all compromised systems were identified, or the full extent of data and service loss. Check Point reported no evidence of destructive activity in the second wave, but that finding does not establish that every targeted organization was unaffected.
It is also not clear from the published details how many ESXi hosts ran destroy_v6 or whether affected organizations recovered all erased data. The described wiper behavior is confirmed in some cases, but the total operational impact remains unknown.
Patch, Inspect, and Track Findings
Organizations using Check Point Security Gateways should apply the November Jumbo Hotfix to Management Servers and gateways, beginning with internet-facing Mobile Access portals. Check Point’s listed minimum takes vary by software release; administrators should match the update to their deployed version rather than assume one take applies to every appliance.
After patching, teams should review every gateway that was exposed against the indicators of compromise in Check Point’s advisory, and assess connected systems, including VMware ESXi hosts, for signs of lateral movement or wiper activity. The source material advises moving unsupported R81.10 and older systems out of service until they can be addressed. U.S. federal agencies face CISA’s November 16 action deadline for CVE-2026-123039.
Further clarity depends on incident investigations and any additional findings from Check Point, CISA or security researchers. For now, the confirmed account covers the attack window, the exploit chain, the reported wiper cases and the available patch guidance; attribution and total impact remain unresolved.
Key Questions
What happened to Check Point Security Gateways?
Check Point says attackers exploited PHP2Shell flaws in unpatched gateways from October 30 to November 4, then used CVE-2026-123039 to gain root access. In some incidents, they moved to VMware ESXi servers and ran a wiper.
What is PHP2Shell?
PHP2Shell is the name used for two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, which CISA says can allow unauthenticated remote code execution. For Check Point appliances, the flaws were reached through the Mobile Access portal.
Did every affected organization face data destruction?
No. Check Point reported wiper activity in some incidents in the first wave targeting Israeli organizations. It said the second wave, which targeted organizations across multiple countries, showed no evidence of destructive activity.
What should Check Point administrators do?
Install the November Jumbo Hotfix on Management Servers and Security Gateways, prioritize internet-facing Mobile Access portals, and inspect exposed devices for the indicators listed in Check Point’s advisory. Administrators should use the take specified for their product release.
Who was behind the attacks?
That remains unconfirmed. Check Point says the evidence does not support a high-confidence assessment. A malware-family link to a China-nexus group has been reported, but the observed targeting and destructive activity do not settle attribution.
Source: ThorstenMeyerAI.com